Trusted Cloud Security Partner

Cloud Security Services That Protect Your Cloud Before an Auditor or an Attacker Finds the Gap

Most cloud breaches don't start with a sophisticated attack. They start with an over-permissive IAM role nobody reviewed, a storage bucket that was opened "temporarily" two years ago, or a logging pipeline that was never switched on in the first place. Cloud moves faster than most security reviews do, so the gap between what your architecture diagram says and what's actually running keeps widening. Our cloud security services close that gap: we assess what you're really exposed to, harden identity, data, and workloads across AWS, Azure, and GCP, and then keep watching so misconfigurations get caught in hours instead of at your next audit.

Cloud Security Services — Cephei Infotech
24/7
Threat Monitoring
3
Clouds Secured
4+
Compliance Frameworks
Trusted by data-driven teams
Our Capabilities

Cloud Security Solutions Built for Multi-Cloud, Compliance-Heavy Environments

Every team reaches a different breaking point. Some just failed a SOC 2 readiness check. Some inherited a cloud account nobody fully understands. Some have alerts firing all day and no idea which three actually matter. Our cloud security services are designed to meet you at whichever point you've hit and get you past it, with security built into how your cloud runs, not layered on top of it afterwards.

INDUSTRY EXPERTISE

Cloud Security Solutions Built Around Your Industry

No two industries carry the same risk, data sensitivity, or regulatory pressure. A fintech platform, a hospital network, and a retail chain can all run on the same cloud provider and still need very different controls. Our cloud security services are shaped around your industry's data types, workflows, uptime requirements, and compliance obligations, from PHI handling and PCI scope reduction to financial audit trails, manufacturing OT connectivity, and customer data protection under GDPR.

Pharmaceuticals
Pharmaceuticals
Clinical trials, manufacturing runs, and regulatory filings all generate data with different rules attached. We build secure analytics that keep compliance reporting audit-ready, forecast demand and supply needs, and give you real-time visibility into plant and trial performance.
Know more →
Building Materials
Building Materials
Distributors in this space live or die by inventory accuracy and dealer performance. Our BI services help you see stock levels across locations, forecast seasonal demand, spot underperforming dealers early, and tighten up supply chain visibility from plant to job site.
Know more →
Wire & Cable
Wire & Cable
Manufacturing downtime is expensive, and quality issues often show up too late to fix cheaply. We build reporting that flags production anomalies as they happen, tracks quality trends line by line, and gives your team the operational data to cut downtime before it compounds.
Know more →
Electronics
Electronics
A single defect can cascade through an entire production run. We help you catch it earlier yield monitoring, component traceability, and predictive maintenance models that flag equipment issues before they cause a line stoppage.
Know more →
Fintech
Fintech
Risk and fraud don't wait for quarterly reviews. Our analytics consulting helps you spot fraud patterns as transactions happen, understand customer behavior at a granular level, and keep regulatory reporting accurate without slowing down your team.
Know more →
Automotive
Automotive
Warranty claims and supplier quality issues are often connected; you just can't always see it. We build reporting that links production data, supplier performance, and warranty trends, plus predictive maintenance models that reduce unplanned downtime on the line.
Know more →
Technology Stack

We work with leading cloud, security, and compliance platforms.

We work across AWS, Azure, and Google Cloud alongside the leading posture management, identity, and detection platforms, selected around your architecture, team skills, and compliance scope rather than a default toolset.

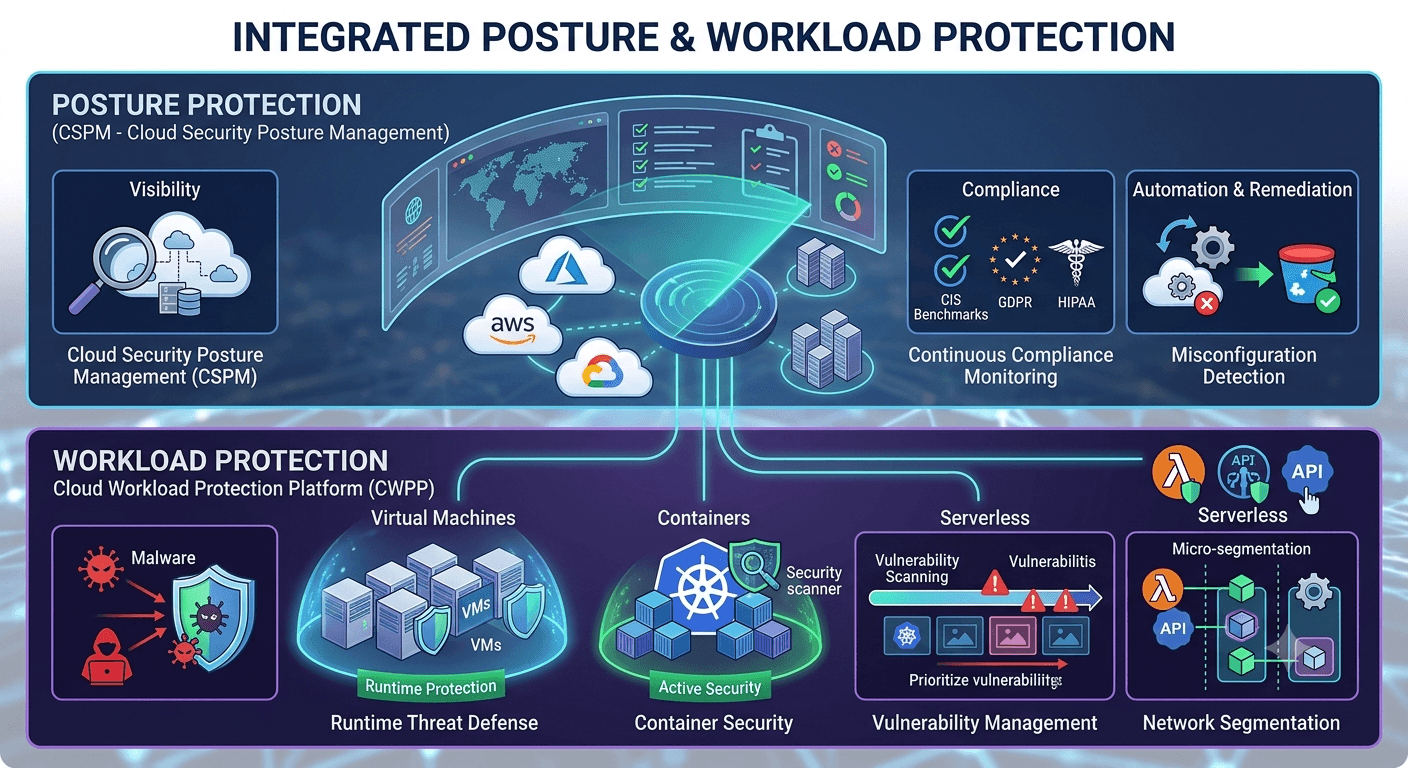
Cloud PlatformsPosture & Workload ProtectionIdentity & Access ManagementDetection, Response & SIEMContainer, IaC & DevSecOps
✦AWS

Broadest native security & IAM tooling

✦Microsoft Azure

Entra ID, Defender & policy governance

✦Google Cloud

Security Command Center & org policies

✦Oracle Cloud

Isolated network security regions

OUR PROCESS

How Do We Secure a Cloud Environment That's Already Running?

We combine assessment, architecture, hands-on remediation, and continuous monitoring to secure cloud environments without stalling delivery. Business risk stays at the center of every step, from the first discovery call through to ongoing operations.

01

Discover & Analyze

We start by understanding what your business needs to solve, where your data currently lives, and what's preventing your team from getting useful insights. This ensures we solve the right problem before building any AI solution.

  • Analyze business goals and objectives
  • Assess existing data sources and infrastructure
  • Define AI project scope, priorities, and timelines
02

Design & Structure

Once we understand the problem, we design the data and AI architecture needed to support it. From data pipelines and storage to model workflows and reporting, every component is planned for scalability and reliability.

  • Design scalable, AI-ready data architecture
  • Plan data pipelines and model workflows
  • Structure dashboards and reporting frameworks
03

Build & Analyze

This is where the solution comes to life. We develop machine learning models, integrate AI-powered analytics capabilities, and rigorously test the results to ensure the insights are accurate, reliable, and useful.

  • Build and train machine learning models
  • Perform rigorous testing and validation
  • Optimize models for performance and accuracy
04

Deploy & Optimize

Deployment is only the beginning. We continuously monitor your AI solution, track model performance, and make improvements as your data, business conditions, and requirements evolve.

  • Deploy AI analytics solutions seamlessly
  • Monitor performance and retrain models
  • Provide ongoing optimization and support
Ready to start?

Turn Cloud Risk Into Cloud Confidence

From security assessments and IAM redesign to CSPM, penetration testing, and 24/7 managed monitoring, we help businesses secure cloud environments that are growing faster than their controls.

WHY CHOOSE US

Why Choose Our Cloud Security Services?

Buying security tools was never the hard part. Value shows up when those tools are configured for your architecture, tuned to your risk, and backed by people who know what a real alert looks like. We combine hands-on cloud engineering, offensive security experience, and compliance knowledge to build protection that holds up under both an audit and an actual attack.

Certified Cloud Security Engineers

Our team holds cloud and security certifications across AWS, Azure, and GCP, and has hardened production environments, not just lab setups. We start with how your business operates, then secure the systems and data that would hurt most if they went down or got out.

24/7Availability

Multi-Cloud & Hybrid Coverage

We secure AWS, Azure, Google Cloud, and hybrid estates under one consistent control model, so policy, identity, and logging don't fragment across providers. As your footprint grows, your security baseline extends with it instead of being rebuilt each time.

3Major Clouds Supported

Security Built Into Your Pipeline

Controls that live outside the delivery process get bypassed. We embed scanning, secrets detection, and infrastructure-as-code checks directly into CI/CD, so issues surface at pull request time rather than in a quarterly report.

100%Shift-Left by Default

Faster Detection & Response

Detection is only useful if someone acts on it. Our monitoring is tuned to reduce false positives and surface the alerts that indicate real attacker behavior, with defined escalation paths and response playbooks agreed before an incident, not during one.

<15minCritical Alert Triage

Audit-Ready Compliance Support

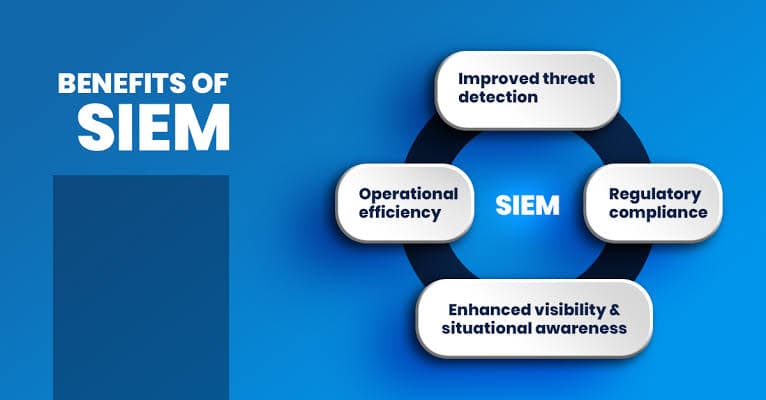
We work against the frameworks you're actually assessed on, SOC 2, HIPAA, GDPR, ISO 27001, mapping controls to real technical evidence. When auditors ask, the proof already exists and is current.

4+Frameworks Supported

Ongoing Security Partnership

Cloud environments change weekly. We continuously review posture, retest after major releases, update detections as new attack techniques emerge, and keep your controls aligned with how your infrastructure looks today.

<24hSupport Response
FAQ

Frequently asked questions

Everything you need to know about working with us.

Cloud security services are the assessment, implementation, and ongoing management of controls that protect cloud infrastructure, identities, applications, and data. In practice that covers configuration and posture management (CSPM), identity and access management, encryption and key management, network segmentation, threat detection and response, and compliance evidence. The goal is straightforward: make sure only the right people and services can reach your cloud resources, and that you'd know quickly if something changed.

Traditional security assumed a perimeter, inside the firewall was trusted, outside wasn't. In the cloud, identity is the perimeter. Resources are created and destroyed through APIs, workloads talk to each other across accounts and regions, and a single over-permissive role can matter more than any firewall rule. Cloud security therefore focuses heavily on IAM, configuration, and continuous monitoring rather than boundary defense alone. It also runs on a shared responsibility model: your provider secures the cloud, you secure what you put in it.

Yes. A cloud security assessment can be a standalone piece of work. We review your cloud accounts, IAM structure, data protection, logging, and network configuration, then hand over a prioritized findings report and remediation roadmap. Plenty of clients take that report and fix things with their own team. That's a perfectly good outcome, and it means any later work is scoped against real evidence rather than guesswork.

It depends on your cloud mix, existing tooling, team size, and compliance scope. A single-cloud team with a small platform group often gets further with native services, AWS Security Hub, Microsoft Defender for Cloud, GCP Security Command Center, than with another dashboard to maintain. Multi-cloud estates usually benefit from a unified CSPM layer such as Wiz or Prisma Cloud. We recommend what fits your environment and who will operate it day to day, not whichever platform is easiest to resell.

It varies with scope and how much of the environment is documented. A focused cloud security assessment typically runs a few weeks. IAM redesign, CSPM rollout, and compliance readiness for SOC 2 or ISO 27001 generally run across several months, largely because remediation has to be sequenced around live systems. After discovery, we give you a realistic timeline tied to your actual account structure, workload count, and audit deadlines.
Let's collaborate

Not Sure Where Your Cloud Is Exposed?

Failed a security questionnaire, inherited an account nobody documented, drowning in alerts, or facing an audit deadline you're not ready for? Tell us where you're stuck, and our cloud security team will help you identify the real risks and the fastest path to closing them.

5,000+Daily Users
9Enterprise Clients
40+Sources Unified